A six-step application security roadmap
Security does not arrive at 100% in one go. Six stages, from laying the foundations at 30% coverage through to zero trust and continuous operation.
Security is not optional any more. But you also cannot protect your applications, infrastructure and cloud environment all at once. What works is a staged approach, taken in order.
Here are six steps for moving coverage from 30% to 100%. Treat the percentages as a rough sense of progress rather than a precise metric.
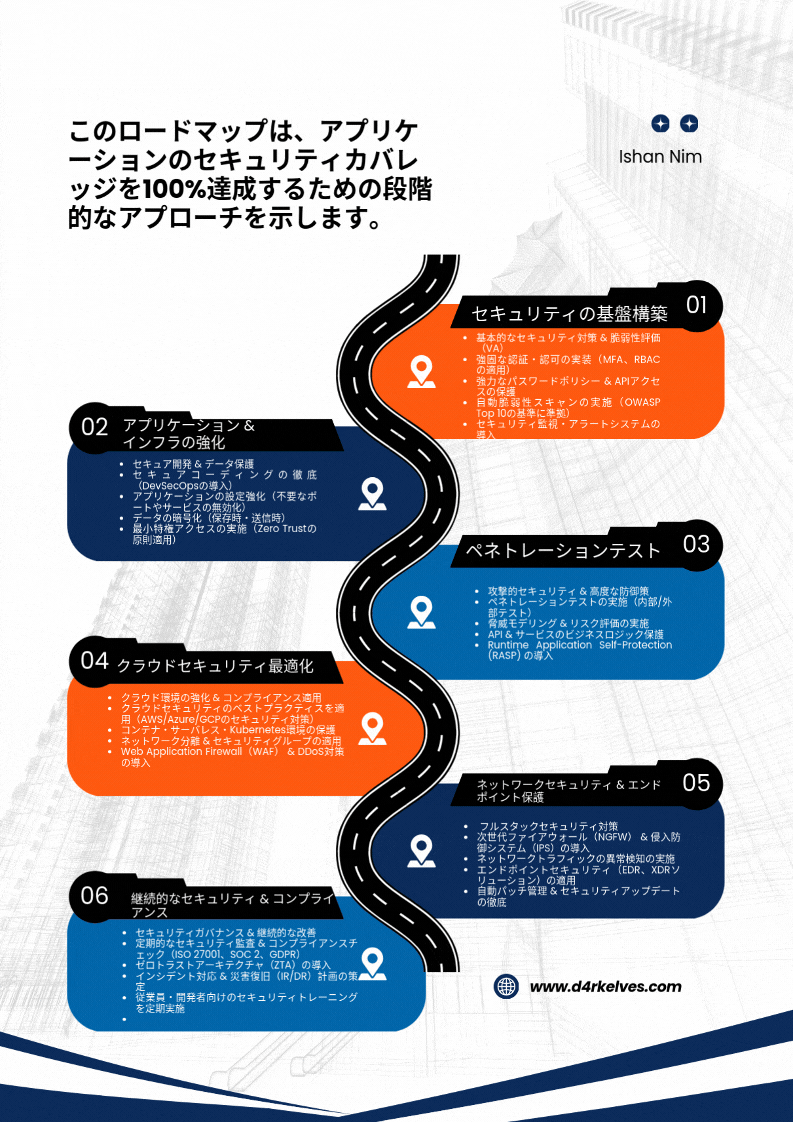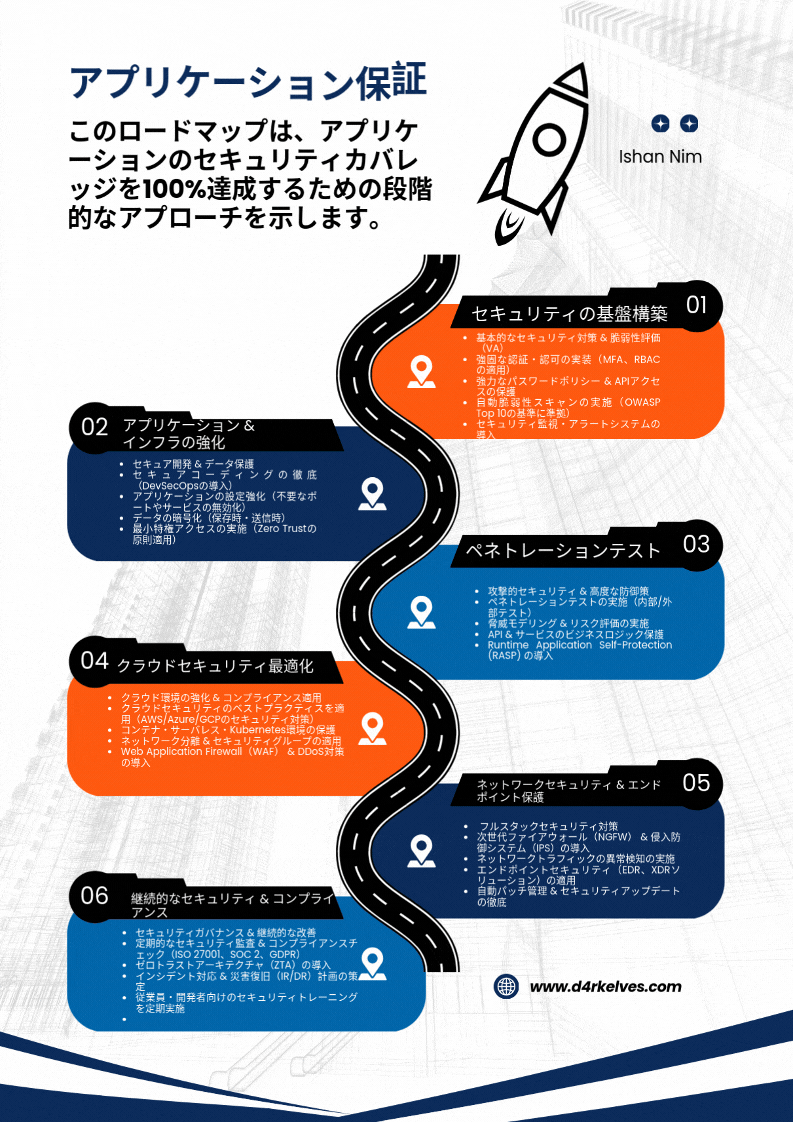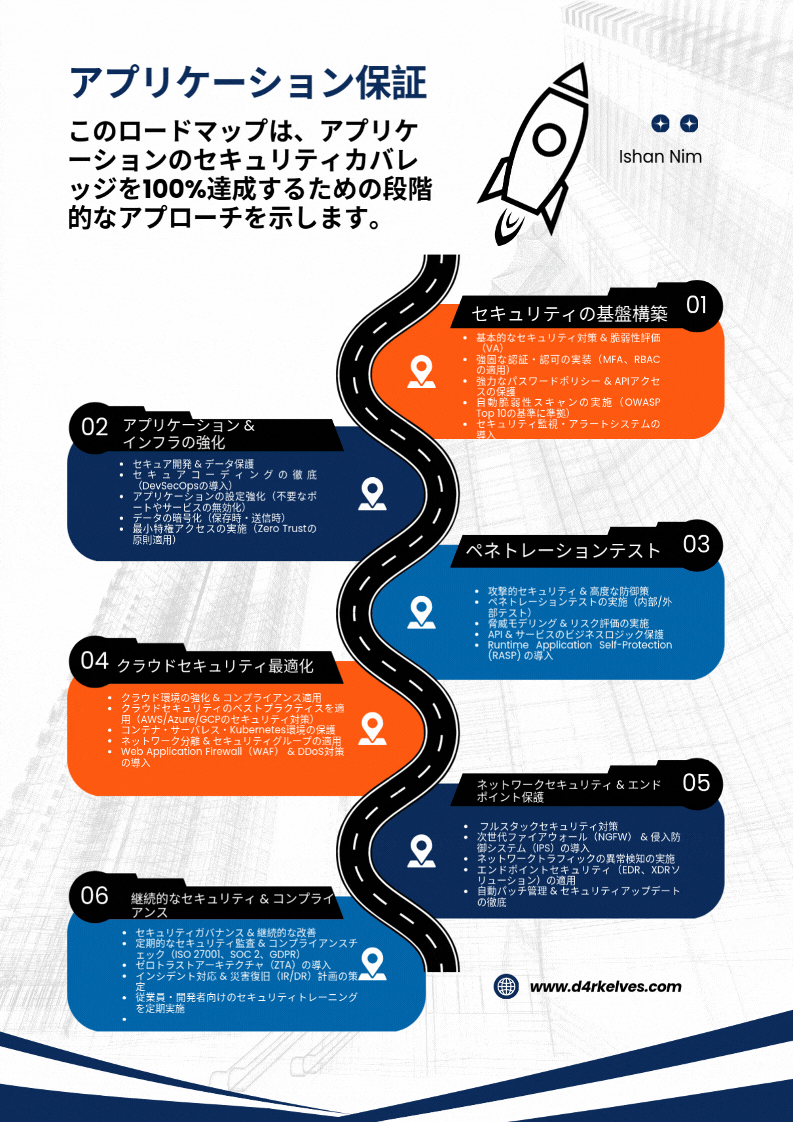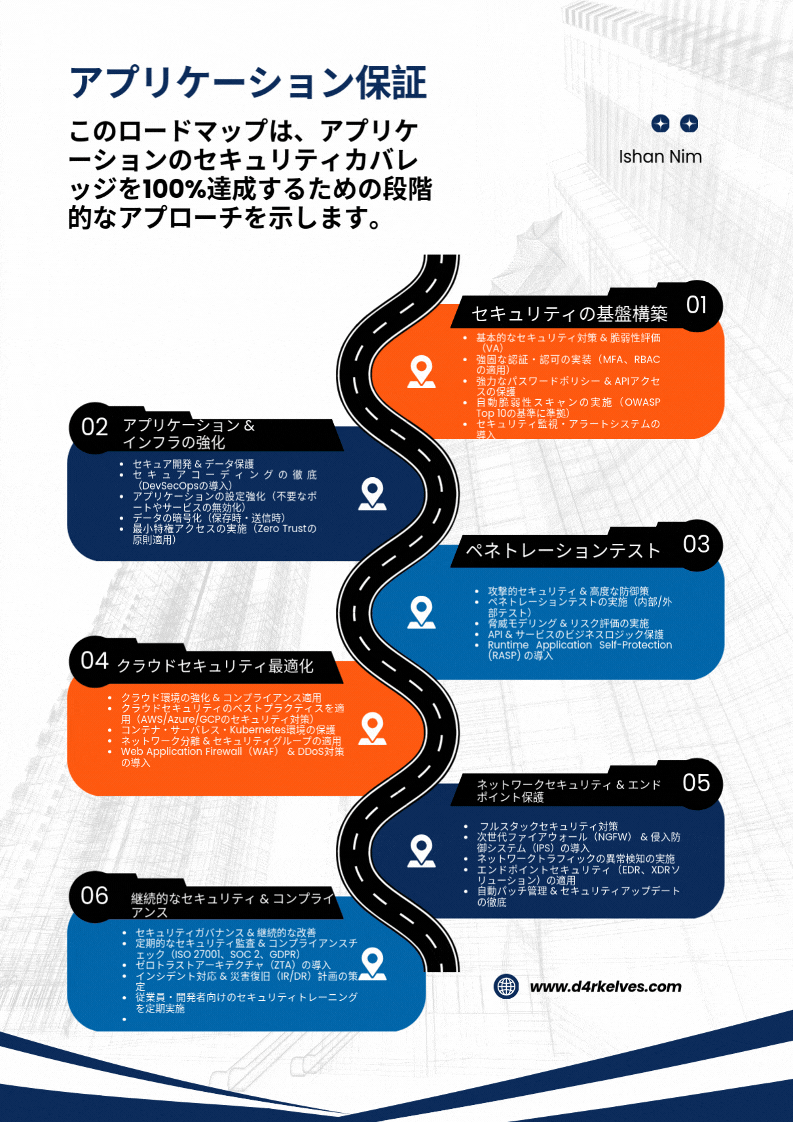
Step 1 — Lay the foundations (~30%)
The first work is unglamorous groundwork, not the interesting controls.
- Strong authentication, with MFA
- Routine vulnerability scanning
- Log collection and security monitoring
Skip this and everything that follows becomes unmeasurable — you will not be able to tell what your later controls are actually protecting.
Step 2 — Harden the app and infrastructure (~50%)
- Secure coding standards, enforced in review rather than in a document
- Encryption of data at rest and in transit
- Least-privilege access, applied properly
By the end of this stage most known vulnerability classes are stopped at the door.
Step 3 — Penetration testing and threat modelling (~70%)
This is where testing turns active.
- Testing from a real attacker’s perspective
- Threat modelling at design time
- Risk assessment and prioritisation of what you find
Scanners only find known problems. Design flaws need a person to go looking.
Step 4 — Optimise cloud security (~90%)
- Continuous review of cloud configuration — misconfiguration remains one of the largest causes of exposure
- API protection and a second look at authorisation design
- DDoS protection and WAF coverage
Step 5 — Network and endpoint protection (~95%)
- Firewalls and segmentation
- Intrusion detection and prevention
- Continuous endpoint monitoring
Step 6 — Continuous management and compliance (100%)
100% does not mean finished. It means running.
- Regular audits
- Migration toward a zero trust architecture
- An incident response capability that has actually been rehearsed
The point
The order matters more than the list. Run a penetration test with no foundations and you have nowhere to put the findings. Build the foundations and never test, and nobody can tell you whether any of it works.
One stage at a time turns out to be the fastest route.
Originally published on Medium · Medium